1. What Does Reading Protected Hexadecimal Data Mean?
Reading PIC18F2450 microprocessor protected heximal refers to examining whether hexadecimal program data can be accessed from a PIC18F2450 microcontroller when its code-protection features are enabled. In embedded system maintenance, this question often arises when engineers need to restore an existing circuit, investigate unexpected behavior, or replicate the software operation of an obsolete electronic device.
The PIC18F2450 belongs to Microchip Technology’s PIC18 family of 8-bit MCUs. Like other Flash-based microcontrollers, it executes machine instructions stored in nonvolatile program memory. These instructions originate from compiled firmware, which may have been developed using C or assembly language before being converted into a programming file.
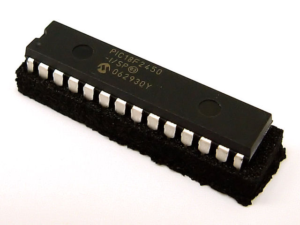
The PIC18F2450 belongs to Microchip Technology’s PIC18 family of 8-bit MCUs. Like other Flash-based microcontrollers, it executes machine instructions stored in nonvolatile program memory. These instructions originate from compiled firmware, which may have been developed using C or assembly language before being converted into a programming file.
A HEX file represents data using hexadecimal notation and includes address information that identifies where particular bytes should be programmed. However, reading a HEX file from an existing archive is different from extracting its contents directly from a physical chip. If the original file is unavailable, engineers must first determine whether the microprocessor permits memory readout.
2. How Code Protection Affects PIC18F2450 Readout
The PIC18F2450 incorporates protective configuration mechanisms that can restrict external access to program memory. These settings are intended to reduce unauthorized copying of firmware and protect application-specific intellectual property.
When the relevant protection configuration is enabled, a conventional programmer may fail to return the original program instructions. This behavior does not necessarily indicate that the IC is damaged. The microcontroller may continue executing its installed software correctly while preventing an external tool from reading the protected memory.
Engineers investigating a locked PIC18F2450 should therefore separate three questions: whether the chip operates, whether its memory can be read, and whether the original firmware remains available elsewhere. These conditions are technically independent.
It is also important not to assume that every protected device uses encrypted storage. Code protection and encryption are different security mechanisms. A secured MCU may restrict readout without encrypting its internal Flash contents. Understanding this distinction helps prevent incorrect conclusions during firmware recovery.
3. Examining Flash Memory and EEPROM Data
A technical assessment should begin with the memory architecture of the PIC18F2450. Program Flash contains the instructions executed by the microprocessor, while data EEPROM provides nonvolatile storage for application information. RAM, in contrast, holds temporary data during operation and generally does not retain its contents after power is removed.
These memory regions have different recovery requirements. A firmware archive might preserve executable instructions but omit EEPROM values, configuration words, or other programming information. Consequently, possessing a valid HEX file does not automatically guarantee a complete reproduction of the original MCU.
During inspection, engineers should identify the addresses represented in the available file and compare them with the device’s documented memory map. The objective is to establish which data regions are present, which are missing, and whether the programming information matches the intended PIC18F2450 configuration.
If a memory dump is available from an authorized source, its integrity can be evaluated by checking record structure, address ranges, and checksums where applicable. Such verification helps distinguish a usable firmware image from a truncated or incorrectly formatted archive.
4. Can Protected Firmware Be Unlocked or Dumped?
The possibility of dumping protected program memory depends on the device’s protection settings and supported programming behavior. Standard read operations may not expose the original instructions when code protection is active.
The word unlock requires particular care in this context. On some microcontrollers, changing protection settings may require a programming operation that also erases existing program memory. Therefore, attempting to unlock a PIC18F2450 without understanding the documented consequences can permanently destroy the firmware being investigated.
A programmer reporting successful communication with the chip does not prove that protected hexadecimal data can be retrieved. Similarly, a successful erase or reprogramming operation does not mean the original software has been recovered.
Before modifying configuration bits or initiating destructive commands, engineers should preserve all existing HEX files and determine whether an earlier firmware archive exists. They should consult the relevant Microchip programming specifications rather than applying generic unlocking procedures intended for other MCU families.
By distinguishing memory readout from firmware replication and source code reconstruction, engineers can evaluate realistic recovery options, preserve available data, and avoid unnecessary destructive operations. This method provides a sound technical foundation for analyzing a locked PIC18F2450 and determining the most appropriate approach to embedded system restoration.
5. Firmware Replication and Source Code Reconstruction
When the required program image is available, engineers can replicate the firmware on a compatible replacement device, provided that the programming requirements and applicable authorization are satisfied. The process involves checking the HEX file, confirming device compatibility, programming the replacement, and testing its behavior in the target circuit.
Source code recovery is a separate challenge. A compiled HEX file generally contains machine instructions rather than the original C source code, comments, variable names, or project files. Disassembly can translate instruction bytes into assembly-language representations, but reconstructing higher-level software requires additional analysis.
For example, engineers may examine control flow, interrupt routines, peripheral configuration, and communication behavior to understand how the original application operates. The resulting reconstruction can support maintenance, although it may not reproduce the original source code exactly.
The same principles apply broadly across Microchip PIC devices and other MCU platforms, including ATMEL microcontrollers. Nevertheless, memory organization and security features vary between product families, so procedures must be selected for the specific IC rather than assumed to be interchangeable.
6. Practical Diagnostic Considerations
A disciplined investigation of a PIC18F2450 should prioritize nondestructive checks. Record the device marking, inspect the circuit for physical damage, identify the programmer and supported device profile, and review any existing firmware archive. Where possible, establish whether the original application can still execute before changing its configuration.
If the chip remains operational but readout is blocked, reproducing its external behavior may be more practical than attempting to recover inaccessible memory. Interface measurements, communication traces, and documented system behavior can help engineers develop a compatible replacement without claiming that the original firmware has been extracted.
Conclusion
Reading PIC18F2450 microprocessor protected heximal requires an understanding of hexadecimal programming files, Flash memory, EEPROM, and microcontroller security configuration. The central technical question is not simply whether a programmer can communicate with the chip, but whether the required firmware data can be accessed without destroying it.
By distinguishing memory readout from firmware replication and source code reconstruction, engineers can evaluate realistic recovery options, preserve available data, and avoid unnecessary destructive operations. This method provides a sound technical foundation for analyzing a locked PIC18F2450 and determining the most appropriate approach to embedded system restoration.