
1. Understanding Hexadecimal Data in the PIC18F2455 Microcontroller
The process of copying hexadecimal data from an MCU PIC18F2455 requires a clear understanding of its memory architecture, firmware organization, and built-in protection mechanisms. The PIC18F2455 is an 8-bit microcontroller developed by Microchip Technology, featuring program Flash memory, data EEPROM, and volatile RAM. These memory regions serve different purposes, and their contents must be evaluated separately during firmware analysis or hardware restoration.
In embedded engineering, the term copy heximal is commonly used to describe copying a hexadecimal firmware file or extracting program data from a microcontroller. Technically, hexadecimal notation represents binary information in a readable format. A HEX file may contain executable instructions, configuration words, addresses, and other programming information required to replicate the original firmware on a compatible chip.
2. Flash, EEPROM, and Firmware Organization
The PIC18F2455 separates program storage from nonvolatile data storage. Its Flash memory contains the executable firmware, including instruction sequences responsible for peripheral control, communication protocols, and application logic. The EEPROM stores persistent application data, such as calibration values, operating parameters, and configuration records.
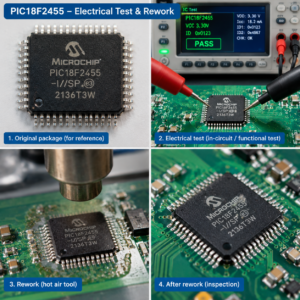
When engineers dump firmware from a microcontroller, they must distinguish between program Flash and EEPROM data. A programmer-generated HEX file may contain one region, several regions, or selected configuration information rather than a complete memory archive.
The source code is another important consideration. A HEX file preserves compiled machine instructions, but it does not ordinarily retain the original C source code, comments, variable names, or development structure. Consequently, firmware replication and source code reconstruction are fundamentally different tasks. Disassembly can help interpret executable instructions, while deeper analysis may be required to understand the original software architecture.
For reliable MCU restoration, engineers should document the memory map, preserve the original firmware archive, and verify that all relevant configuration settings have been recorded.
3. Can Locked PIC18F2455 Firmware Be Dumped?
One of the main challenges in copying a PIC18F2455 is determining whether its protective settings restrict program-memory readout. Microchip microcontrollers provide code-protection mechanisms intended to prevent unauthorized access to stored instructions. When the relevant protection bits are enabled, a programmer may be unable to retrieve the original program Flash contents through normal read commands.
It is important to distinguish a locked device from a damaged chip. A microcontroller can execute its application normally while refusing external readout. Similarly, a secured device may accept certain programming operations without exposing its existing firmware.
The ability to dump data therefore depends on the specific protection configuration, device condition, and supported programming operations. Unlocking should not be assumed to be a simple software procedure. Depending on the device and operation, erasing protected memory may destroy the very firmware that an engineer intends to recover.
Before attempting any operation, engineers should identify the exact device, consult the applicable Microchip programming documentation, and determine whether a verified backup already exists. Unauthorized bypass attempts may also conflict with intellectual-property rights or device security requirements.
4. Replicating Firmware Without Losing Critical Information
Successful firmware replication requires more than copying a sequence of hexadecimal characters. Engineers must verify the target chip, memory addresses, configuration words, oscillator settings, and other device-specific parameters.
For the PIC18F2455, configuration settings can affect clock operation, reset behavior, peripheral functions, and protection features. An incomplete HEX file may therefore produce a microcontroller that accepts programming but fails to operate like the original circuit.
A controlled workflow begins with preserving available programming files and recording the original hardware configuration. The next step is to inspect the HEX records for valid addresses and consistent data, followed by programming a compatible replacement device when the required contents are legitimately available.
After programming, functional testing should cover the interfaces and peripherals used by the application. For example, USB communication, timing behavior, and input/output responses may need to be compared against the original hardware. This approach provides stronger evidence of successful replication than relying solely on a programmer’s completion message.
5. Why Firmware Recovery Is Different From Source Code Recovery
Firmware analysis frequently involves several distinct objectives: reading memory, recovering application behavior, reconstructing source code, and reproducing an operational microcontroller. These objectives require different techniques and do not necessarily produce the same results.
A readable HEX archive can support programming and disassembly, but it cannot automatically restore the original development project. Likewise, extracting EEPROM data does not guarantee that the corresponding firmware can be recovered. Encrypted storage, protected memory, missing configuration information, or physical damage can introduce additional obstacles, although encryption should not be assumed to be present on every PIC18F2455 device.
The same general distinction applies when comparing Microchip PIC devices with other MCU families, including certain ATMEL microcontrollers. Protection mechanisms, memory organization, programming interfaces, and recovery limitations vary by device. Procedures suitable for one IC should not be transferred to another microprocessor without confirming its technical documentation.
6. Technical Conclusion
Copying hexadecimal firmware from a PIC18F2455 is primarily a memory-access, data-integrity, and compatibility problem. Engineers must determine which Flash, EEPROM, and configuration contents are available before deciding whether the original software can be replicated.
The most reliable approach is to preserve existing HEX files, verify their memory coverage, examine the device’s protective settings, and validate the programmed replacement through functional testing. If the original MCU is locked and no backup exists, complete firmware recovery may not be possible through ordinary programming operations.
Ultimately, understanding the difference between firmware replication, memory dumping, source code reconstruction, and protection removal is essential for accurate technical analysis. A structured evaluation of the PIC18F2455 helps engineers distinguish recoverable data from inaccessible memory and avoid destructive operations that could permanently eliminate valuable firmware information.