Read IC PIC16LF747 Heximal
Read IC PIC16LF747 Heximal out from its flash memory after reverse engineering microcontroller PIC16LF747 and figure out the MCU circuitry scheme for the location of security
Read IC PIC16LF747 Heximal out from its flash memory after reverse engineering microcontroller PIC16LF747 and figure out the MCU circuitry scheme for the location of security
The PIC16F737 stands as a highly resilient 28-pin architecture engineered by Microchip, favored by hardware developers for its integrated 10-bit Analog-to-Digital Converter (ADC), three independent

Read Chip ATMEGA861P Code out from its memory and disable the security fuse bit by focus ion beam technology, recover MCU content out from the
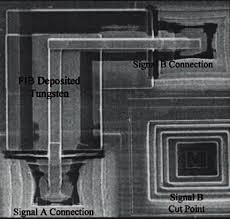
Read IC PIC16F636 Flash program and Eeprom data out and download the firmware to other blank MCU PIC16F636, microcontroller reverse engineering technique include microcomputer decapsulation,
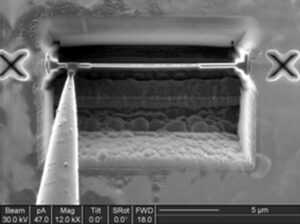
Read Microcontroller ATMEGA2560L Code out from the memory which include flash content and eeprom data, the status of MCU ATmega2560L can be turned from encrypted
Read MCU ATMEGA2560PV Heximal out from its memory and then copy the firmware to blank Microcontroller ATmega2560, original Microprocessor ATmega2560 will be decapsulate and tamper
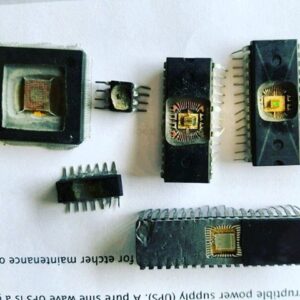
Read MCU PIC12F629 Archive from microcontroller PIC12F629 program memory and data eeprom, this process can help to recover firmware from Microprocessor memory through MCU crack
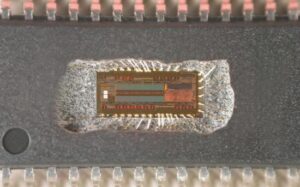
Read Chip ATmega640PV Binary from flash memory and eeprom memory, status of microcontroller ATmega640PV will be broken and conten readout from processor memory; In Clear