Maintaining active operation across complex electronic installations often hinges on keeping legacy control systems running smoothly. When an unrecorded hardware error jeopardizes a vital control board, the ability to extract microcontroller pic16f883 file assets serves as a powerful solution for sustaining system performance. The PIC16F883 by Microchip is an efficient 28-pin 8-bit architecture packed with 4K words of flash memory, 256 bytes of EEPROM, a 256-byte SRAM matrix, and an integrated 11-channel 10-bit analog-to-digital converter.
この高度な技術プロセスは、元の Microchip PIC16F883 microcontroller に搭載された主要な Flashプログラムメモリと補助的な EEPROMセルのデータを取得するために慎重に実施されます。これらのメモリ領域は、システム全体の完全なデータアーカイブを構成します。
この組み込み命令セットを正常に取得することで、技術者は元のソースコードへアクセスすることなく、システム動作を再構築し、機能的なソフトウェア依存関係を分析できます。
標準デバッグインターフェースを制限するため、純正の Microchip PIC16F883 microprocessor には内部セキュリティビットが使用されています。そのため、完全なデータ取得には、基盤となる Microchip PIC16F883 microcontroller の firmware を消去することなく、読み取り制限を処理する専門的な低レベル技術が必要となります。
Engineered with flexible power-saving modes and wide operating voltage tolerances, hardware designers historically integrated this specific microchip device into automated fluid metering stations, commercial HVAC fan speed controllers, remote environmental monitoring nodes, and precision industrial weigh scales. When these field-deployed devices suffer physical breakdown or their original developmental documentation becomes lost over time, facility administrators need a safe, reliable technique to extract the underlying control code to avoid costly total-system replacements and mitigate unplanned operational downtime.
All other EUSART control bits are assumed to be in their default state. Setting the CREN bit of the RCSTA register enables the receiver circuitry of the EUSART. Clearing the SYNC bit of the TXSTA register configures the EUSART for asynchronous operation. Setting the SPEN bit of the RCSTA register enables the EUSART and automatically configures the RX/DT I/O pin as an input. If the RX/DT pin is shared with an analog peripheral the analog I/O function must be disabled by clearing the corresponding ANSEL bit.
이 정밀한 기술 과정은 원본 Microchip PIC16F883 microcontroller의 주요 Flash program memory와 보조 EEPROM cells에 저장된 데이터를 확보하기 위해 신중하게 수행되며, 이 두 영역은 함께 시스템 전체 데이터 아카이브를 구성합니다.
이 임베디드 명령 집합을 성공적으로 분리하면 기술자는 원본 소스 코드에 접근하지 않고도 시스템 동작을 재구성하고 기능적 소프트웨어 의존성을 분석할 수 있습니다.
기본 Microchip PIC16F883 microprocessor는 표준 디버그 인터페이스를 차단하기 위해 내부 보안 비트를 사용하므로, 완전한 데이터 확보를 위해서는 Microchip PIC16F883 microcontroller의 firmware가 완전히 삭제되는 상황을 방지하면서 읽기 제한을 관리하는 전문적인 저수준 기술이 필요합니다.
Acquiring complete functional instructions from a secured, protected, or locked semiconductor requires an intricate understanding of physical microelectronic defenses. When specialists attempt to extract, recover, or restore system logic from an encrypted silicon layout, their main goal is to isolate the raw binary or heximal file stored deep within the internal hardware registers. This delicate procedure is carefully executed to dump both the primary flash program memory and the auxiliary eeprom cells, which together form the complete data archive of the machine.
Successfully isolating this embedded instruction set enables technicians to rebuild system behavior and analyze functional software dependencies without requiring access to the original source code. Because the native microprocessor deploys internal security bits to block standard debug interfaces, obtaining a clean dump requires specialized low-level techniques to bypass the read bans without triggering a catastrophic erasure of the underlying firmware.
Overcoming these internal hardware defenses presents severe technical challenges and demands extreme precision during execution. Factory security schemes on a secured chip utilize buried anti-tamper meshes, power-glitch detectors, and voltage monitoring circuits designed to permanently erase the internal flash and eeprom storage arrays if unexpected probing is identified.
Эта сложная техническая процедура выполняется тщательно для получения информации из основной программной памяти Flash и вспомогательных ячеек EEPROM оригинального Microchip PIC16F883 microcontroller, которые вместе формируют полный архив данных системы.
Успешное выделение встроенного набора инструкций позволяет техническим специалистам восстановить поведение системы и анализировать функциональные зависимости программного обеспечения без доступа к исходному коду.
Поскольку оригинальный Microchip PIC16F883 microprocessor использует внутренние защитные биты для блокировки стандартных интерфейсов отладки, получение полной копии данных требует специализированных низкоуровневых методов обработки ограничений чтения без критического удаления firmware внутри Microchip PIC16F883 microcontroller.
If an unauthorized tool introduces improper electrical tolerances or timing delays during an extraction attempt, the target microprocessor will instantly lock down or destroy its stored data archive. Why do corporate clients take on these delicate risks to open or hack a protected microcontroller? The necessity arises because original component vendors routinely go out of business, discontinue legacy product lines, or refuse to release proprietary code, leaving critical commercial infrastructure completely stranded whenever a single chip experiences a hardware fault.
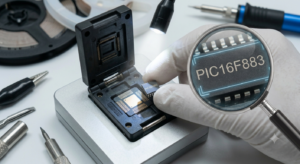
यह संवेदनशील तकनीकी प्रक्रिया सावधानीपूर्वक इस प्रकार संचालित की जाती है कि मूल Microchip PIC16F883 microcontroller की मुख्य Flash program memory और सहायक EEPROM cells दोनों से डेटा प्राप्त किया जा सके, जो मिलकर मशीन का संपूर्ण डेटा संग्रह बनाते हैं।
इस एम्बेडेड निर्देश सेट को सफलतापूर्वक अलग करने से तकनीशियन सिस्टम के व्यवहार को पुनर्निर्मित कर सकते हैं और मूल स्रोत कोड तक पहुँच के बिना कार्यात्मक सॉफ़्टवेयर निर्भरताओं का विश्लेषण कर सकते हैं।
क्योंकि मूल Microchip PIC16F883 microprocessor मानक डिबग इंटरफेस को रोकने के लिए आंतरिक सुरक्षा बिट्स का उपयोग करता है, इसलिए एक साफ डेटा कॉपी प्राप्त करने के लिए विशेष निम्न-स्तरीय तकनीकों की आवश्यकता होती है, ताकि पढ़ने की सीमाओं को संभाला जा सके और Microchip PIC16F883 microcontroller के firmware को पूरी तरह मिटने से बचाया जा सके।
Ultimately, obtaining a pristine binary or heximal file through controlled reverse engineering delivers immense operational resilience and financial advantages to our clients. Having unrestricted access to the firmware archive gives maintenance departments the freedom to clone obsolete controllers onto modern circuit assemblies, patch hidden software bugs, and ensure seamless system interoperability across the plant. This proactive technical capability changes an inaccessible, locked hardware barrier back into a fully transparent digital asset—drastically lowering operational overhead, eliminating vendor lock-in, and extending the service life of high-value industrial equipment for years to come.
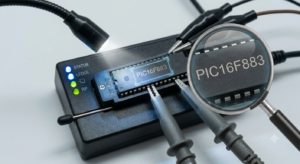
يتم تنفيذ هذه العملية التقنية الدقيقة بعناية من أجل جمع بيانات كل من ذاكرة برنامج Flash الأساسية وخلايا EEPROM الإضافية من Microchip PIC16F883 microcontroller الأصلي، حيث تشكل هاتان المنطقتان معاً أرشيف البيانات الكامل للنظام.
يسمح عزل مجموعة التعليمات المدمجة هذه بنجاح للفنيين بإعادة بناء سلوك النظام وتحليل الاعتماديات البرمجية الوظيفية دون الحاجة إلى الوصول إلى الكود المصدري الأصلي.
وبما أن Microchip PIC16F883 microprocessor الأصلي يستخدم وحدات حماية داخلية لمنع واجهات التصحيح القياسية، فإن الحصول على نسخة بيانات كاملة يتطلب تقنيات متخصصة منخفضة المستوى للتعامل مع قيود القراءة دون التسبب في مسح كامل لبرنامج firmware الخاص بـ Microchip PIC16F883 microcontroller.