The PIC16F886 is a versatile 8-bit microcontroller from Microchip that combines substantial embedded functionality with a practical architecture for control-oriented products. It provides flash program memory, data EEPROM, analog-to-digital conversion, timers, communication capabilities, and configurable I/O, allowing it to perform considerably more than simple switching or timing operations. Because of this combination of features, the MCU has been used in industrial instruments, electronic measurement equipment, motor and process controllers, power supplies, security equipment, automotive auxiliary electronics, and consumer products. In an established product, the PIC16F886 can contain years of accumulated engineering work in the form of firmware, configuration parameters, calibration information, and program logic. When that original software is unavailable, the physical chip may therefore become an important source for recovering information needed to maintain the product.
عبارت **کپیکردن حافظه فلش PIC16F886 قفلشده** به یک نیاز تخصصی برای **بازیابی برنامه داخلی** اشاره دارد، نه برنامهنویسی معمولی MCU. هنگامی که یک **PIC16F886** اصلی **ایمنسازیشده**، **محافظتشده** یا **قفلشده** باشد، تجهیزات متداول برنامهریزی ممکن است امکان دسترسی به **حافظه فلش داخلی** آن را فراهم نکنند. در یک پروژه **بازیابی مجاز**، مهندسان میتوانند بررسی کنند که آیا از نظر فنی امکان **نفوذ**، **استخراج**، **بازیابی**، **باز کردن** یا **بازگردانی** محتوای **میکروکنترلر PIC16F886** وجود دارد، در حالی که از تغییر غیرضروری **تراشه** اصلی جلوگیری شود. بسته به پیکربندی **ریزپردازنده PIC16F886**، اطلاعات موردنظر میتواند شامل **firmware**، اطلاعات مرتبط با **کد منبع**، **دادههای باینری**، دادههای برنامه **هگزادسیمال**، محتوای **EEPROM**، اطلاعات پیکربندی و سایر **دادههای تعبیهشده** باشد. یک **دامپ حافظه** کنترلشده از **میکروکنترلر PIC16F886** میتواند یک **فایل** یا **آرشیو** ارزشمند برای تحلیلهای بعدی فراهم کند. از آنجا که بازیابی **MCU PIC16F886** محافظتشده شامل مکانیزمهای امنیتی است، این کار بهعنوان یک سرویس تخصصی **مهندسی معکوس سختافزار و برنامه داخلی** انجام میشود و بر حفظ یکپارچگی دادهها تمرکز دارد، نه افشای جزئیات روشهای عبور از سازوکارهای حفاظتی.
When reading 9-bit data from the receive FIFO buffer, the RX9D data bit must be read before reading the 8 Least Significant bits from the RCREG. A special Address Detection mode is available for use when multiple receivers share the same transmission line, such as in RS-485 systems. Address detection is enabled by setting the ADDEN bit of the RCSTA register.
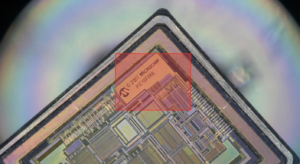
The phrase copy locked PIC16F886 flash describes a specialized firmware-recovery requirement rather than routine MCU programming. When an original device is secured, protected, or locked, conventional programming equipment may not provide access to its internal flash memory. For an authorized recovery project, engineers may investigate whether it is technically feasible to hack, extract, recover, open, or restore the contents of the microcontroller while avoiding unnecessary alteration of the original chip. Depending on the device configuration, the information of interest can include firmware, source code-related information, binary, heximal program data, EEPROM contents, configuration information, and other embedded data.
A controlled memory dump can provide a valuable file or archive for subsequent analysis. Because protected MCU recovery involves security mechanisms, the work is approached as a specialized hardware and firmware reverse engineering service, with emphasis on data integrity rather than disclosure of detailed protection-bypass procedures.
Upon receiving an address character, user software determines if the address matches its own. Upon address match, user software must disable address detection by clearing the ADDEN bit before the next Stop bit occurs. When user software detects the end of the message, determined by the message protocol used, software places the receiver back into the Address Detection mode by setting the ADDEN bit.
Initialize the SPBRGH, SPBRG register pair and the BRGH and BRG16 bits to achieve the desired baud rate (see Section 12.3 “EUSART Baud Rate Generator (BRG)”).
One of the principal difficulties is that a locked PIC16F886 does not necessarily behave like an ordinary programmable memory device. Protection settings can restrict read access, while an encrypted or otherwise transformed data representation may create additional analysis requirements. Engineers must also distinguish between the contents of flash program memory and EEPROM, because the two areas can contain fundamentally different types of information. A firmware dump may contain executable program instructions rather than human-readable source code, meaning additional reverse engineering may be necessary to understand its functionality.
Physical condition is another variable: an aging microchip, damaged PCB connection, unstable power supply, or previously modified circuit can affect the reliability of data acquisition. Consequently, attempting to recover a locked MCU requires assessment of the device, preservation of the original hardware, controlled extraction, and subsequent validation of the recovered binary or heximal archive. Not every secured device is recoverable, and the feasibility depends on the exact silicon revision, protection configuration, physical condition, and available engineering evidence.
For equipment manufacturers and owners, successful recovery can have a practical impact far beyond obtaining a copy of a program. A verified flash file may allow a company to manufacture replacement control boards, refurbish discontinued equipment, investigate field failures, or preserve a mature product while its original development team is no longer available. EEPROM data can also be valuable when calibration coefficients, configuration parameters, or product-specific settings are required for proper operation.
**لاک شدہ PIC16F886 فلیش کو کاپی کرنا** عام MCU پروگرامنگ کے بجائے ایک خصوصی **فرم ویئر ریکوری کی ضرورت** کو بیان کرتا ہے۔ جب اصل **PIC16F886** **محفوظ**، **تحفظ یافتہ** یا **لاک شدہ** ہو، تو روایتی پروگرامنگ آلات اس کی اندرونی **فلیش میموری** تک رسائی فراہم کرنے کے قابل نہیں ہو سکتے۔ ایک **مجاز ریکوری منصوبے** میں انجینئرز یہ جائزہ لے سکتے ہیں کہ اصل **چِپ** میں غیر ضروری تبدیلی کیے بغیر **PIC16F886 مائیکروکنٹرولر** کے مواد کو **ہیک** کرنا، **نکالنا**، **بازیافت کرنا**، **کھولنا** یا **بحال کرنا** تکنیکی طور پر ممکن ہے یا نہیں۔ **PIC16F886 مائیکروپروسیسر** کی ترتیب کے مطابق مطلوبہ معلومات میں **فرم ویئر**، **سورس کوڈ سے متعلق معلومات**، **بائنری پروگرام ڈیٹا**، **ہیکسا ڈیسیمل پروگرام ڈیٹا**، **EEPROM** کا مواد، کنفیگریشن کی معلومات اور دیگر **اندرونی طور پر شامل ڈیٹا** شامل ہو سکتا ہے۔ ایک کنٹرول شدہ **PIC16F886 مائیکروکنٹرولر میموری ڈمپ** بعد کے تجزیے کے لیے ایک قیمتی **فائل** یا **آرکائیو** فراہم کر سکتا ہے۔ چونکہ محفوظ **PIC16F886 MCU** کی ریکوری میں حفاظتی میکانزم شامل ہوتے ہیں، اس لیے اس کام کو ایک خصوصی **ہارڈویئر اور فرم ویئر ریورس انجینئرنگ سروس** کے طور پر انجام دیا جاتا ہے، جس میں تفصیلی حفاظتی رکاوٹوں کو عبور کرنے کے طریقہ کار ظاہر کرنے کے بجائے ڈیٹا کی سالمیت پر زور دیا جاتا ہے۔
The recovered firmware archive can serve as a reference when migrating an application from the PIC16F886 to a newer microcontroller or microprocessor, while reverse engineering can help engineers understand the relationship between the program and surrounding circuitry. For businesses with large installed bases of legacy equipment, this approach can reduce unnecessary redesign costs and prevent functional products from becoming unusable simply because their original software resources have disappeared. Ultimately, recovering information from a protected PIC16F886 provides a pathway for preserving embedded engineering assets, supporting long-term maintenance, and extending the useful life of established electronic products.